118filers, current period
80the period before
21controls it touches
15frameworks
Privacy Compliance in 10-K and 10-Q filings, by month.
The marked line is the first month any public company in our record used the phrase; everything left of it is nobody writing it down.
Companies disclosing it
118
wrote this into a filing with the SEC
What it obligates
21
controls across 15 frameworks whose text speaks to it
Employers hiring for it
2,655
open US roles name it, and the ones below are hiring now
The long view, in annual and quarterly filings
A 10-K or 10-Q is a periodic report, so this counts how often the phrase appears in routine annual and quarterly reporting. It moves far more slowly and the numbers are larger.
Every month since 2008. The last point is the current month and is still
filling, so it always looks lower than it will be.
2008
peak 116 in February 2026
2026
Share this finding
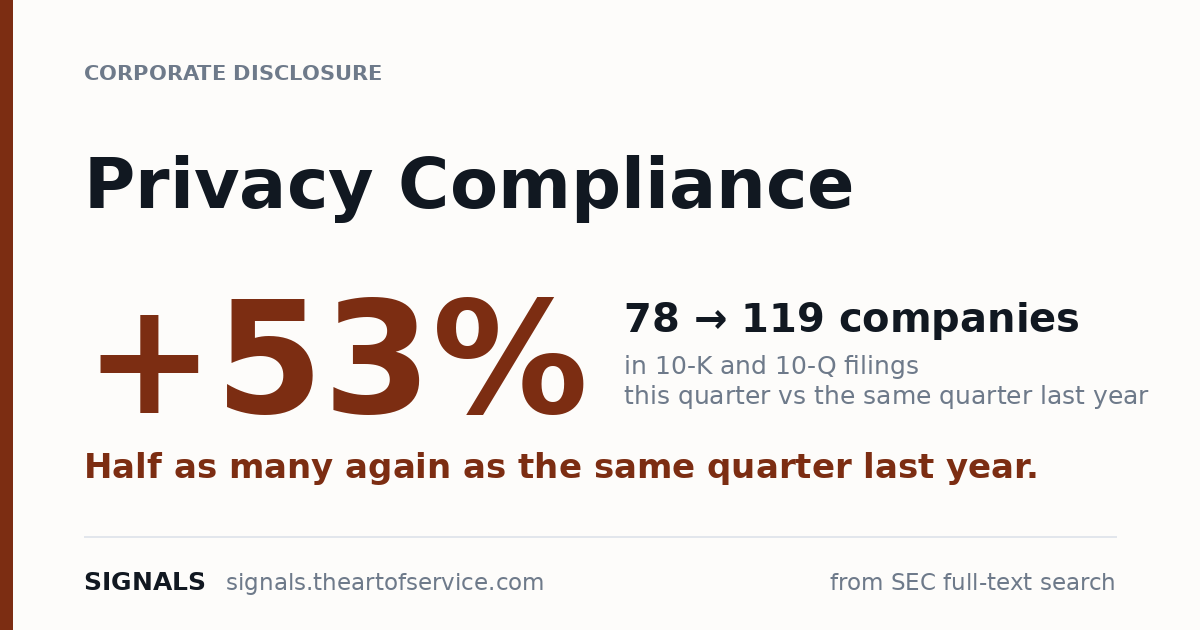
Noticeably more than the same quarter last year. The card below carries the whole finding, so it makes
sense to somebody who never clicks through.
Who disclosed it
From SEC full-text search over 8-K filings. Every row links to the filing itself.
| Company | Form | Filed | |
|---|
| TANDEM DIABETES CARE INC TNDM | 8-K | 2026-11-05 | filing |
| Solidion Technology Inc. STI | 8-K | 2026-11-09 | filing |
| Four Leaf Acquisition Corp | 8-K | 2026-09-02 | filing |
| Data443 Risk Mitigation, Inc. ATDS | 8-K | 2026-09-02 | filing |
| VALLEY NATIONAL BANCORP | 8-K | 2026-09-28 | filing |
| Chiron Real Estate Inc. | 8-K/A | 2026-11-05 | filing |
| Rank One Computing Corp ROC | 8-K | 2026-09-30 | filing |
| REGIS CORP RGS | 8-K | 2026-11-05 | filing |
| House of Doge Inc. HODO | 8-K | 2026-10-23 | filing |
| 8X8 INC /DE/ EGHT | 8-K | 2026-09-09 | filing |
| GOLUB CAPITAL BDC, Inc. GBDC | 8-K | 2026-11-17 | filing |
| WHIRLPOOL CORP /DE/ | 8-K | 2026-10-26 | filing |
| OCULUS INC. OVTZ | 10-Q | 2026-11-10 | filing |
| Meta Platforms, Inc. META | 10-Q | 2026-10-22 | filing |
| USANA HEALTH SCIENCES INC USNA | 10-Q | 2026-11-12 | filing |
The full search on EDGAR
Who is hiring for it
A sample of the open roles naming this phrase. An employer paying a salary
against something is the least ambiguous demand signal there is, and every row links to the
posting so the claim can be checked rather than believed. The total above is the whole US
market; these are the ones we hold the posting for.
| Role | Posted |
|---|
| Business Technology Partner, Customer and Growth Magnolia Oil & Gas Corp · Waco, TX | 2026-11-19 |
| Senior Security Auditor Roblox Corp · Gurugram, Haryana, India | 2026-11-17 |
| Legal Counsel - EMEA Applied Digital Corp. · Stuttgart | 2026-11-16 |
| Legal Counsel - EMEA Applied Digital Corp. · Munich | 2026-11-16 |
| Legal Counsel - EMEA Applied Digital Corp. · London | 2026-11-16 |
| Principal Security & Privacy Compliance Architect Zscaler, Inc. · Santa Clara, California, USA | 2026-11-11 |
| Senior US Legal Counsel Arq, Inc. · New York | 2026-11-06 |
| Senior Security Auditor Roblox Corp · San Mateo, CA, United States | 2026-10-28 |
| Team Lead, Software Development Engineering (Communications Platform) CarGurus, Inc. · Boston, Massachusetts, United States | 2026-10-27 |
| Sr. Lead Counsel, Privacy PINTEREST, INC. · Remote, US | 2026-10-23 |
| Senior GTM Systems Analyst (Marketing IT) Zscaler, Inc. · Santa Clara, California, USA | 2026-10-23 |
| Principal, Marketing Analytics Elastic N.V. · United States | 2026-10-22 |
| Engineering Manager, Workday SoFi Technologies, Inc. · San Francisco, California | 2026-10-19 |
| Senior Solutions Engineer, Advertisers and Agencies PubMatic, Inc. · New York, US | 2026-10-08 |
Which industries file it
Companies grouped by the industry classification on their own filing. A count, not a
survey.
| Industry | | Companies |
|---|
| Chemicals and pharmaceuticals | | 81 |
| Software and IT services | | 74 |
| Not classified | | 65 |
| Banking | | 25 |
| Holding and investment offices | | 20 |
| Instruments and medical devices | | 18 |
| Health services | | 17 |
| Electronics and electrical equipment | | 17 |
| Services and entertainment | | 17 |
| Insurance | | 16 |
What it obligates
Our corpus holds 21 controls across
15 frameworks whose text speaks to this. Not a judgement:
these controls say so, and each is one lookup from its source document. Ordered by how much each
framework has to say about it, so the one that will cost you the most work is first. Every name
opens that framework in the corpus.
What an auditor will ask you to produce
The artefacts named on those controls, most frequently cited first.
- Role inventory + RACI
- Assessment, authorization, and monitoring policy
- Access control policy
- Procedures addressing system connections
- System and communications protection policy
- Module compliance + remediation
- Supervisory dialogue records
- privacy programme plan and staffing
How it usually fails
Recorded when each control was verified against its source. This is where programmes
that think they are covered turn out not to be.
- Roles undefined
- Internal connections are established without prior security and privacy compliance checks of the components
- Compliance check results are not recorded before internal connections are approved
- Module compliance gaps
- Supervisory engagement weak
- privacy folded into security with no distinct assessment work
CCPA/CPRA holds 95 controls. They appear again inside
16 other frameworks in our corpus; the 10 strongest are shown. Thickness and
size both carry the number of controls shared, so work done once counts in every framework on
this diagram.
79If you already run CCPA/CPRA, that is the 79 controls behind this disclosure, already evidenced.
138And ISO 27701:2019 is not a separate programme. 138 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
60And CNIL Guidance on Employee Monitoring and Workplace Video Surveillance is not a separate programme. 60 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
60And UK ICO Employment Practices and Data Protection: Monitoring Workers (2023) is not a separate programme. 60 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
Run as two programmes
217 controls
CCPA/CPRA and ISO 27701:2019 scoped separately, each with its own
evidence, its own owner and its own budget line. This is how almost everybody does it.
Run once, counted twice
138 already done
138 of ISO 27701:2019's controls are controls you evidenced for
CCPA/CPRA. Same artefacts, same owner, no second effort. The mapping is the
only reason anybody knows.
Privacy Compliance in 10-K and 10-Q filings, by month.
The marked line is the first month any public company in our record used the phrase; everything left of it is nobody writing it down.
What this actually means
- Why now
- 118 public companies wrote this into an 8-K in the last seven days, 48% more than the seven before. That is not sentiment or a survey. It is a count of companies choosing to put a phrase into a document they are legally accountable for.
- Who already cares
- 2,655 open US roles name this work today, which suggests increased attention to it beyond what any filing says. A job advertisement clears a budget holder and a filing clears legal, so the two answer to different people. We have not measured which moves first, only that both are moving.
- What comes into scope
- Once the phrase is on the record it maps to obligations within CCPA/CPRA, GDPR, Netherlands GDPR Implementation Act (UAVG. 250 controls behind those, and the difference between asserting them and evidencing them is the whole of the work.
- Who is quietly ahead
- Anyone already running CCPA/CPRA has done 138 of the controls that carry ISO 27701:2019 too. Same evidence, second standard. Most organisations run those as two programmes with two budgets because nobody told them the mapping existed.
- Who is exposed
- 10 companies disclosed this for the first time in the last ninety days, out of 462 in total. A first mention is a company deciding it can no longer not say it. Whoever has not yet is either genuinely unaffected or has not looked, and nothing here distinguishes the two.
What this obligates
The instruments in our corpus that govern this disclosure, and how many controls sit
behind each. This is not a filing count. It is what applies once a company has written the
phrase down.
8 frameworks, 250 controls between them.
CCPA/CPRA holds 95 controls. They appear again inside
16 other frameworks in our corpus; the 10 strongest are shown. Thickness and
size both carry the number of controls shared, so work done once counts in every framework on
this diagram.
What closing it also moves
The same controls appear in other frameworks through mappings held in our corpus. Work
done here is already progress there. This is the part that is not in EDGAR and not in any public
dataset: it comes from mappings built and verified by hand, control by control.
ISO 27701:2019138
CNIL Guidance on Employee Monitoring and Workplace Video Surveillance60
UK ICO Employment Practices and Data Protection: Monitoring Workers (2023)60
Germany Federal Data Protection Act (BDSG)59
Article 29 Working Party Opinion 2/2017 on Data Processing at Work (WP249)46
UK ICO Guidance on Video Surveillance including CCTV (2022)40
EDPB Guidelines 3/2019 on Processing of Personal Data through Video Devices39
ISO 27002:202237
Counted as controls reached through cross-framework mappings. It measures
overlap of work, not compliance with the named framework.
Run as two programmes
217 controls
CCPA/CPRA and ISO 27701:2019 scoped separately, each with its own
evidence, its own owner and its own budget line. This is how almost everybody does it.
Run once, counted twice
138 already done
138 of ISO 27701:2019's controls are controls you evidenced for
CCPA/CPRA. Same artefacts, same owner, no second effort. The mapping is the
only reason anybody knows.
79If you already run CCPA/CPRA, that is the 79 controls behind this disclosure, already evidenced.
138And ISO 27701:2019 is not a separate programme. 138 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
60And CNIL Guidance on Employee Monitoring and Workplace Video Surveillance is not a separate programme. 60 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
60And UK ICO Employment Practices and Data Protection: Monitoring Workers (2023) is not a separate programme. 60 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
Tell me when Privacy Compliance files something new
One email when a public company newly discloses this, naming the company and what our corpus says it puts in scope. Nothing else, and one click to stop.
Where this comes from
The left half is public record: SEC full-text search over 8-K filings, counted across a
14 day window against the equivalent window before it. You can check
every row.
The right half is ours: 723 frameworks and
20,473 controls, 531 of those frameworks verified against
their source documents, with the auditor evidence and common failure modes recorded control by
control. Controls appear here because their own text names this term.
Cite this
The Art of Service Signals. Privacy Compliance corporate disclosure activity: 118 filers against 80 in the prior period, in 10-K and 10-Q filings, this quarter against the same quarter last year. Accessed 22 November 2026. https://signals.theartofservice.com/t/privacy-compliance/
Free to use with attribution, no permission needed. The chart downloads as an SVG
with the source printed on it. If you cite it we would like to know, but you do not need to
ask.
Today's edition ·
How programmes fail ·
The obligation index