120filers, current period
160the period before
325controls it touches
92frameworks
Internal Control in 10-K and 10-Q filings, by month.
The phrase was already in use in the first month we hold, so this shows how it has moved since rather than when it began.
Companies disclosing it
120
wrote this into a filing with the SEC
What it obligates
325
controls across 92 frameworks whose text speaks to it
Employers hiring for it
34,741
open US roles name it, and the ones below are hiring now
The long view, in 8-K filings
An 8-K is filed within four business days of an event, so this counts filings made because something happened.
Every month since 2008. The last point is the current month and is still
filling, so it always looks lower than it will be.
2008
peak 757 in November 2021
2026
Share this finding
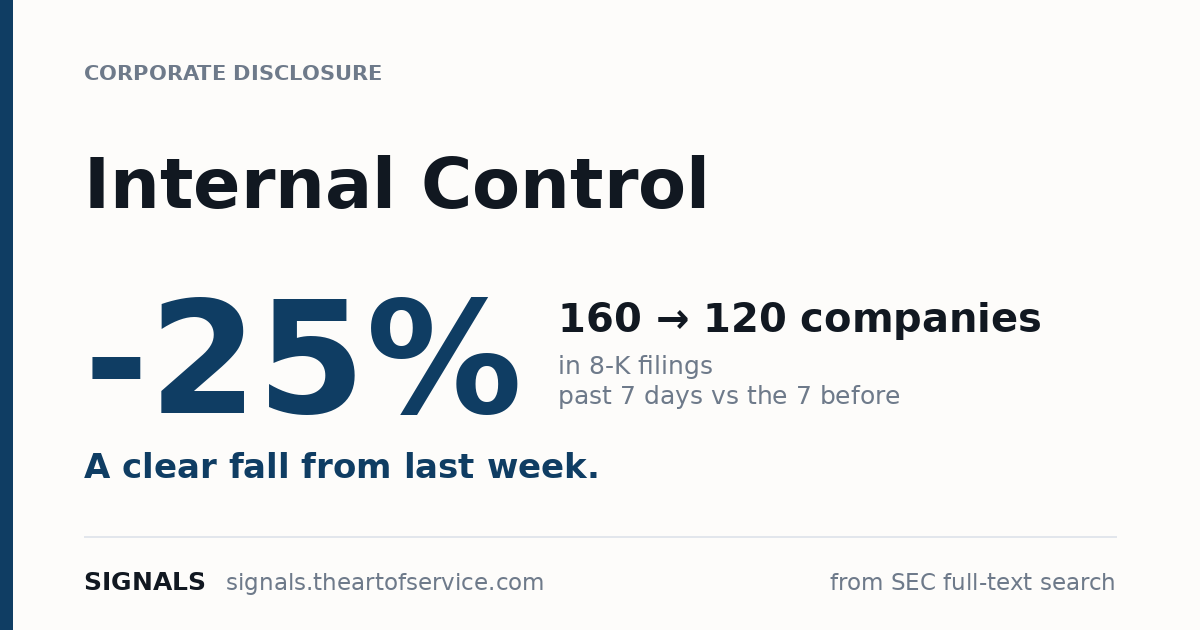
A clear fall from last week. The card below carries the whole finding, so it makes
sense to somebody who never clicks through.
Who disclosed it
From SEC full-text search over 8-K filings. Every row links to the filing itself.
| Company | Form | Filed | |
|---|
| CENTURY CASINOS INC /CO/ CNTY | 8-K | 2026-11-16 | filing |
| TALOS ENERGY INC. TALO | 8-K/A | 2026-11-19 | filing |
| Aspira Women's Health Inc. AWHL | 8-K | 2026-11-16 | filing |
| OZ VISION INC. OZVN | 8-K | 2026-11-16 | filing |
| Brand Engagement Network Inc. | 8-K | 2026-11-17 | filing |
| AIB Data Centers Inc. AIB | 8-K | 2026-11-17 | filing |
| Beeline Holdings, Inc. BLNE | 8-K | 2026-11-19 | filing |
| Forefront Tech Holdings Acquisition Corp | 8-K | 2026-11-20 | filing |
| Standard Nuclear, Inc. STDN | 8-K | 2026-11-17 | filing |
| LINCOLN NATIONAL LIFE INSURANCE CO /IN/ | 8-K | 2026-11-16 | filing |
| PIONEER POWER SOLUTIONS, INC. PPSI | 8-K | 2026-11-17 | filing |
| Solaris Energy Infrastructure, Inc. SEI | 8-K/A | 2026-11-16 | filing |
The full search on EDGAR
Who is hiring for it
A sample of the open roles naming this phrase. An employer paying a salary
against something is the least ambiguous demand signal there is, and every row links to the
posting so the claim can be checked rather than believed. The total above is the whole US
market; these are the ones we hold the posting for.
| Role | Posted |
|---|
| Senior SEC Reporting Accountant Coinbase Global, Inc. · Remote - USA | 2026-11-20 |
| Manager, Treasury Accounting CoreWeave, Inc. · Dallas, TX / Livingston, NJ / New York, NY / Sunnyvale, CA / San Francisco, CA / Bellevue, WA | 2026-11-20 |
| Senior Director, Global Payroll IonQ, Inc. · Remote, US | 2026-11-20 |
| Internal Audit Manager Robinhood Markets, Inc. · Luxembourg, Luxembourg (Bitstamp) | 2026-11-20 |
| (Senior) NetSuite Developer Verve Therapeutics, Inc. · Dublin, Ireland | 2026-11-20 |
| Internal Auditor I (2027 Early Career Program) Affirm Holdings, Inc. · New York, New York, United States | 2026-11-19 |
| Senior Staff Accountant fuboTV Inc. /FL · New York, NY | 2026-11-19 |
| Payroll Specialist Rush Street Interactive, Inc. · Chicago | 2026-11-19 |
| Senior Manager Tax Compliance Operations Volta Inc. · London, UK | 2026-11-19 |
| Senior Payroll Associate Zeta Global Holdings Corp. · Hyderabad, India | 2026-11-19 |
| Europe Regional Controller AST SpaceMobile, Inc. · Barcelona, Spain | 2026-11-18 |
| Manager, GL Accounting Cloudflare, Inc. · In-Office | 2026-11-18 |
| Senior Analyst - Procurement Operations COMMVAULT SYSTEMS INC · Bangalore, India | 2026-11-18 |
| Vice President, Accounting FARADAY FUTURE INTELLIGENT ELECTRIC INC. · El Segundo, California, United States | 2026-11-18 |
How it actually arrives
An 8-K's meaning is in its item number, not its text. These are the items the filings
containing this phrase were filed under. The first group is something that happened to the
company. The second is the phrase turning up in the ordinary course of reporting, most often in
an earnings release, which is a very different thing and is usually the larger number.
| Filed because something happened |
Companies |
|---|
| Other material event Item 8.01 | 4959 |
| Director or officer departure Item 5.02 | 2133 |
| Change of accountant Item 4.01 | 1219 |
| Financial statements no longer reliable Item 4.02 | 883 |
| Delisting or listing rule failure Item 3.01 | 269 |
| Bankruptcy or receivership Item 1.03 | 57 |
| Material impairment Item 2.06 | 26 |
| Material cybersecurity incident Item 1.05 | 1 |
| Mentioned in routine reporting |
Companies |
|---|
| Financial statements and exhibits Item 9.01 | 7149 |
| Entry into a material agreement Item 1.01 | 5423 |
| Regulation FD disclosure Item 7.01 | 2947 |
| Results of operations, the earnings release Item 2.02 | 1164 |
| Completion of an acquisition Item 2.01 | 1144 |
| Shareholder vote Item 5.07 | 241 |
This is why a headline count on its own overstates the case.
Where the routine number dominates, the phrase is being tracked as language rather than as
events.
Which industries file it
Companies grouped by the industry classification on their own filing. A count, not a
survey.
| Industry | | Companies |
|---|
| Holding and investment offices | | 1470 |
| Chemicals and pharmaceuticals | | 1071 |
| Banking | | 568 |
| Software and IT services | | 515 |
| Instruments and medical devices | | 345 |
| Mining and extraction | | 294 |
| Electronics and electrical equipment | | 282 |
| Retail | | 258 |
| Industrial machinery | | 235 |
| Services and entertainment | | 232 |
What it obligates
Our corpus holds 325 controls across
92 frameworks whose text speaks to this. Not a judgement:
these controls say so, and each is one lookup from its source document. Ordered by how much each
framework has to say about it, so the one that will cost you the most work is first. Every name
opens that framework in the corpus.
What an auditor will ask you to produce
The artefacts named on those controls, most frequently cited first.
- Board charter
- Control matrix
- Policies mapped to COSO 17 principles
- Risk assessment workpapers
- Internal and external communication evidence
- Fraud risk assessment results
- Code of conduct
- Org structure document
How it usually fails
Recorded when each control was verified against its source. This is where programmes
that think they are covered turn out not to be.
- Principles not mapped
- Fraud assessment skipped
- Communication ad hoc
- Changes lack analysis
- Code not communicated
- Board not independent
ISO 27001:2022 Evidence & Implementation Kit
118 controls sit behind ISO 27001:2022, and this is the documentation set for them: an adopt-ready artifact per control, and the evidence an auditor asks for against each.
See what is in it, $249
The same set every buyer of this kit receives. Nothing here is produced on request.
118If you already run ISO 27001:2022, that is the 118 controls behind this disclosure, already evidenced.
346And ISO 27701:2019 is not a separate programme. 346 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
177And COBIT 2019 is not a separate programme. 177 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
165And ISO 27002:2022 is not a separate programme. 165 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
Run as two programmes
464 controls
ISO 27001:2022 and ISO 27701:2019 scoped separately, each with its own
evidence, its own owner and its own budget line. This is how almost everybody does it.
Run once, counted twice
346 already done
346 of ISO 27701:2019's controls are controls you evidenced for
ISO 27001:2022. Same artefacts, same owner, no second effort. The mapping is the
only reason anybody knows.
Internal Control in 10-K and 10-Q filings, by month.
The phrase was already in use in the first month we hold, so this shows how it has moved since rather than when it began.
What this actually means
- Why now
- 120 public companies wrote this into an 8-K in the last seven days, 25% fewer than the seven before. That is not sentiment or a survey. It is a count of companies choosing to put a phrase into a document they are legally accountable for.
- Who already cares
- 34,741 open US roles name this work today, which suggests increased attention to it beyond what any filing says. A job advertisement clears a budget holder and a filing clears legal, so the two answer to different people. We have not measured which moves first, only that both are moving.
- What comes into scope
- Once the phrase is on the record it maps to obligations within ISO 27001:2022, ISO 27001:2013, COSO Internal Control. 255 controls behind those, and the difference between asserting them and evidencing them is the whole of the work.
- Who is quietly ahead
- Anyone already running ISO 27001:2022 has done 346 of the controls that carry ISO 27701:2019 too. Same evidence, second standard. Most organisations run those as two programmes with two budgets because nobody told them the mapping existed.
- Who is exposed
- 100 companies disclosed this for the first time in the last ninety days, out of 7241 in total. A first mention is a company deciding it can no longer not say it. Whoever has not yet is either genuinely unaffected or has not looked, and nothing here distinguishes the two.
What this obligates
The instruments in our corpus that govern this disclosure, and how many controls sit
behind each. This is not a filing count. It is what applies once a company has written the
phrase down.
4 frameworks, 255 controls between them.
ISO 27001:2022 holds 123 controls. They appear again inside
122 other frameworks in our corpus; the 10 strongest are shown. Thickness and
size both carry the number of controls shared, so work done once counts in every framework on
this diagram.
What closing it also moves
The same controls appear in other frameworks through mappings held in our corpus. Work
done here is already progress there. This is the part that is not in EDGAR and not in any public
dataset: it comes from mappings built and verified by hand, control by control.
ISO 27701:2019346
COBIT 2019177
ISO 27002:2022165
ISO/IEC 42001:2023160
ISO 22301:2019154
PCI DSS 4.0102
NIS2 Directive86
Counted as controls reached through cross-framework mappings. It measures
overlap of work, not compliance with the named framework.
Run as two programmes
464 controls
ISO 27001:2022 and ISO 27701:2019 scoped separately, each with its own
evidence, its own owner and its own budget line. This is how almost everybody does it.
Run once, counted twice
346 already done
346 of ISO 27701:2019's controls are controls you evidenced for
ISO 27001:2022. Same artefacts, same owner, no second effort. The mapping is the
only reason anybody knows.
118If you already run ISO 27001:2022, that is the 118 controls behind this disclosure, already evidenced.
346And ISO 27701:2019 is not a separate programme. 346 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
177And COBIT 2019 is not a separate programme. 177 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
165And ISO 27002:2022 is not a separate programme. 165 of its controls are the same controls. If it is on next year's plan, that part of it is already done.
Tell me when Internal Control files something new
One email when a public company newly discloses this, naming the company and what our corpus says it puts in scope. Nothing else, and one click to stop.
Where this comes from
The left half is public record: SEC full-text search over 8-K filings, counted across a
7 day window against the equivalent window before it. You can check
every row.
The right half is ours: 723 frameworks and
20,473 controls, 531 of those frameworks verified against
their source documents, with the auditor evidence and common failure modes recorded control by
control. Controls appear here because their own text names this term.
Cite this
The Art of Service Signals. Internal Control corporate disclosure activity: 120 filers against 160 in the prior period, in 8-K filings over seven days against the seven before. Accessed 22 November 2026. https://signals.theartofservice.com/t/internal-control/
Free to use with attribution, no permission needed. The chart downloads as an SVG
with the source printed on it. If you cite it we would like to know, but you do not need to
ask.
Today's edition ·
How programmes fail ·
The obligation index